security
CVE-2026-110142: Use-after-free in Chrome's FileSystem
- severity
- Medium
- component
- Use-after-free in FileSystem
- reported
- Google Chrome VRP,
- status
- fixed in Chrome 155.0.8059.79 (stable)
- write-up
- generic pass
Chrome release, Chrome 155 stable ↗ Chromium bug 553525515 ↗ NVD record ↗
In August 2026 I reported another use-after-free in Chrome’s FileSystem, the same part of Chrome as my June bug. Google rated this one Medium, assigned CVE-2026-110142, and shipped the fix in Chrome 155.0.8059.79 on October 13.
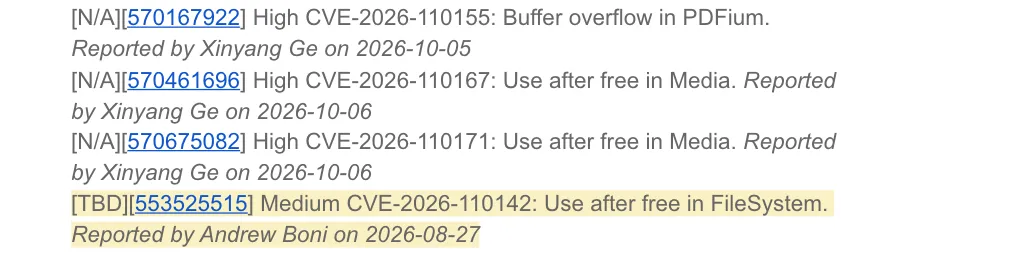
Same class as June, too. Chrome frees a piece of memory, then goes back and uses it anyway. June’s was rated Critical. This one’s Medium, even though the CVE record says a crafted page could run code outside the sandbox. Why it landed at Medium is the interesting part, and it waits with the rest.
The bug itself is still restricted. Chrome keeps the details locked until most people have the fix, and I’m playing by the same rule. What gets freed, and how a page gets there, comes later.
Timeline#
- 2026-08-27: reported to the Chrome VRP (Chromium issue 553525515)
- 2026-10-13: Chrome 155.0.8059.79 to stable; the advisory publishes, rated Medium
- 2026-10-13: NVD record published