security
CVE-2026-59618: Out-of-bounds read in the Google Pixel's JPEG encoder
- severity
- Moderate
- component
- Out-of-bounds read in Pixel JPEG (SMFC)
- reported
- Android VRP,
- status
- fix in progress
Android security acknowledgements ↗ Android Security Bulletins ↗ Android & Google Devices VRP ↗
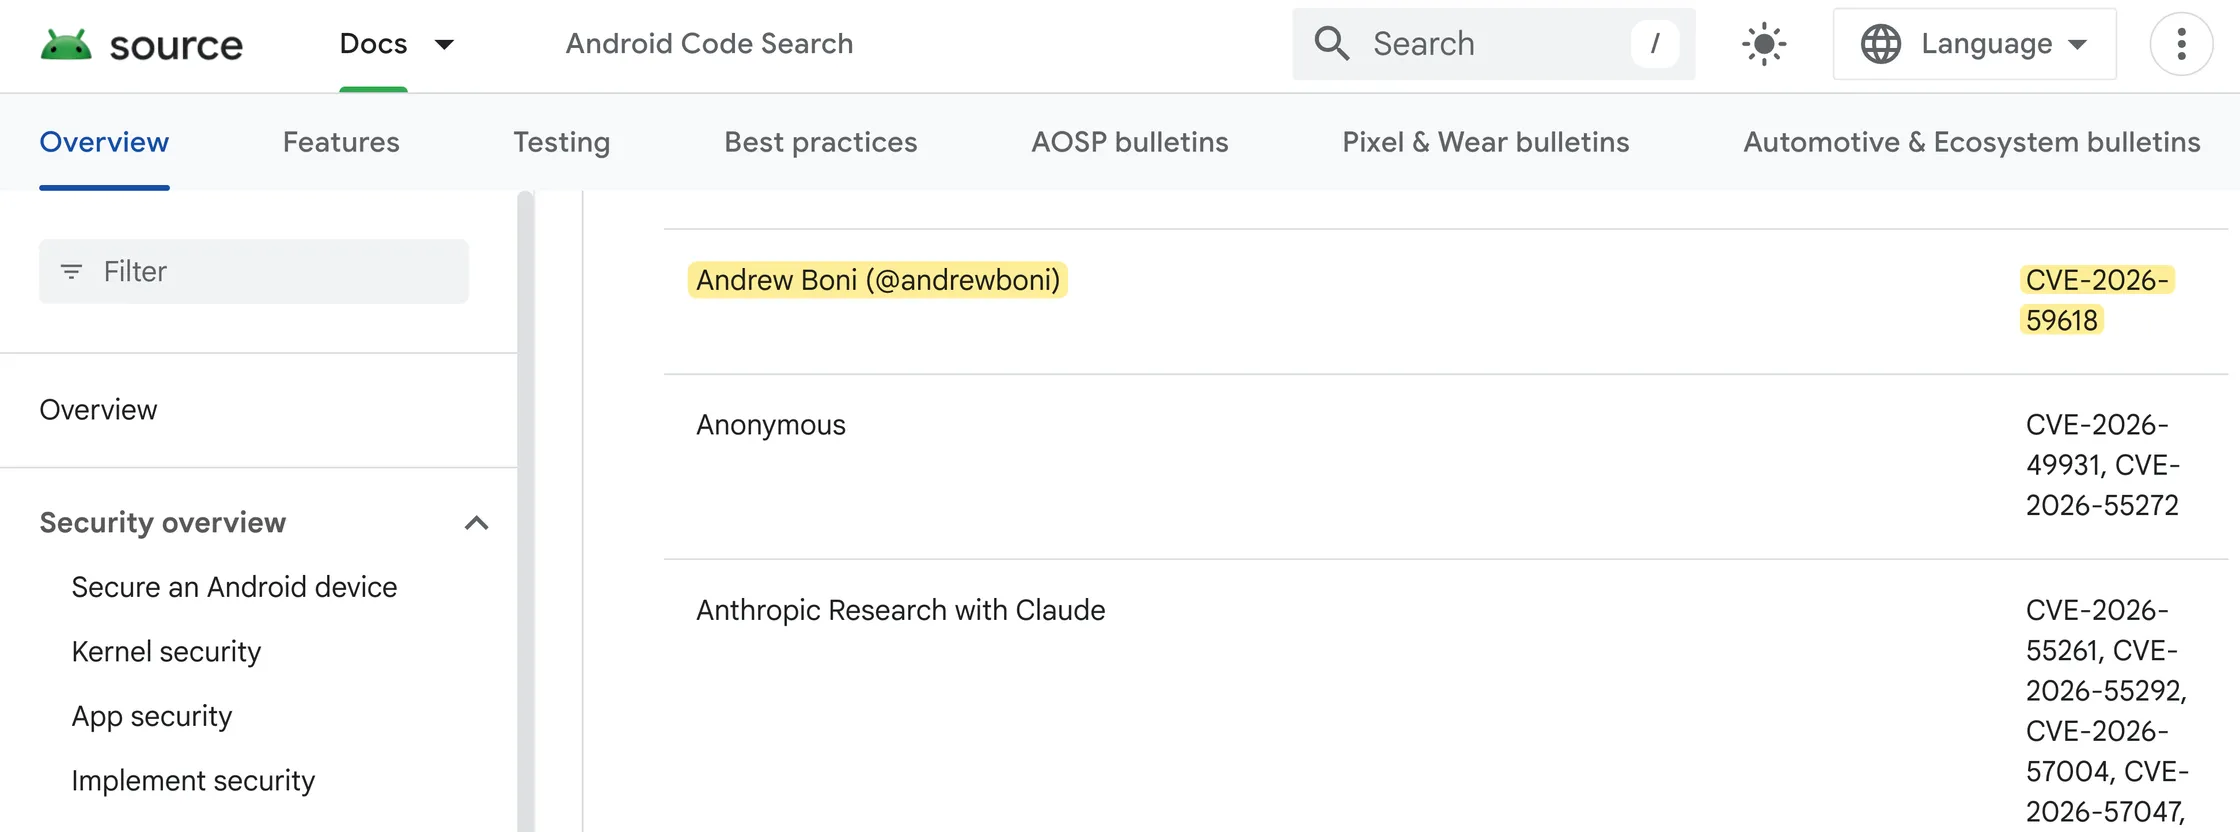
In April 2026 I reported a bug in the Pixel’s hardware JPEG encoder to Android’s VRP. Google assigned it CVE-2026-59618 and rated it a Moderate severity vulnerability. In November, Android credited me for it in its security acknowledgements.
The encoder is a small piece of hardware called SMFC and it has a single job: take a camera frame and turn it into a JPEG, quickly.
Here, I was able to find a way to get it to read data outside the frame.
Timeline#
- 2026-04-27: reported to the Android VRP
- 2026-06-22: rated Moderate
- 2026-10-13: CVE-2026-59618 assigned
- 2026-11-02: credited in Android’s security acknowledgements, under November 2026