security

CVE-2026-21094: Out-of-bounds write in Galaxy Wi-Fi

severity
High
component
Out-of-bounds write in wpa_supplicant
reported
Samsung Mobile Security Rewards Program,
status
fixed in SMR Sep-2026 Release 1
write-up
generic pass

Samsung bulletin, September 2026 ↗ NVD record ↗

On an Android phone, wpa_supplicant is the userspace half of Wi-Fi. It finds a network, joins it, and keeps the link up by listening to access points and acting on what they say.

In June 2026, I reported an out-of-bounds write in it on Samsung Galaxy phones. Samsung tracked it as SVE-2026-3217, assigned CVE-2026-21094, rated it High, and shipped the fix in SMR Sep-2026 Release 1.
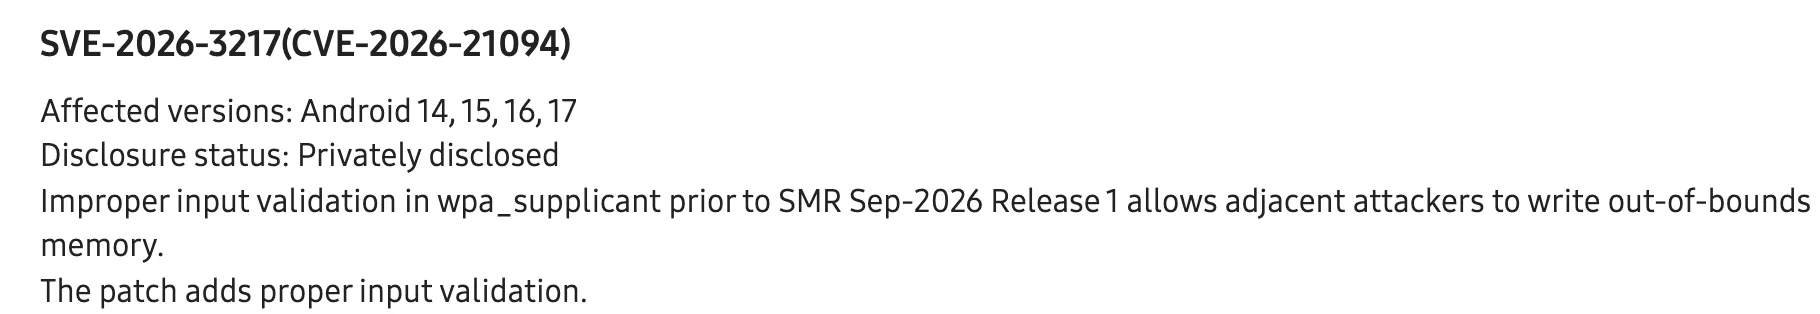
The Samsung bulletin entry for SVE-2026-3217 (CVE-2026-21094), listing affected versions Android 14, 15, 16 and 17, disclosure status "Privately disclosed", one sentence describing improper input validation in wpa_supplicant, and one sentence describing the patch
Samsung's half of the public record. Samsung's number, the affected Android versions, and two sentences.
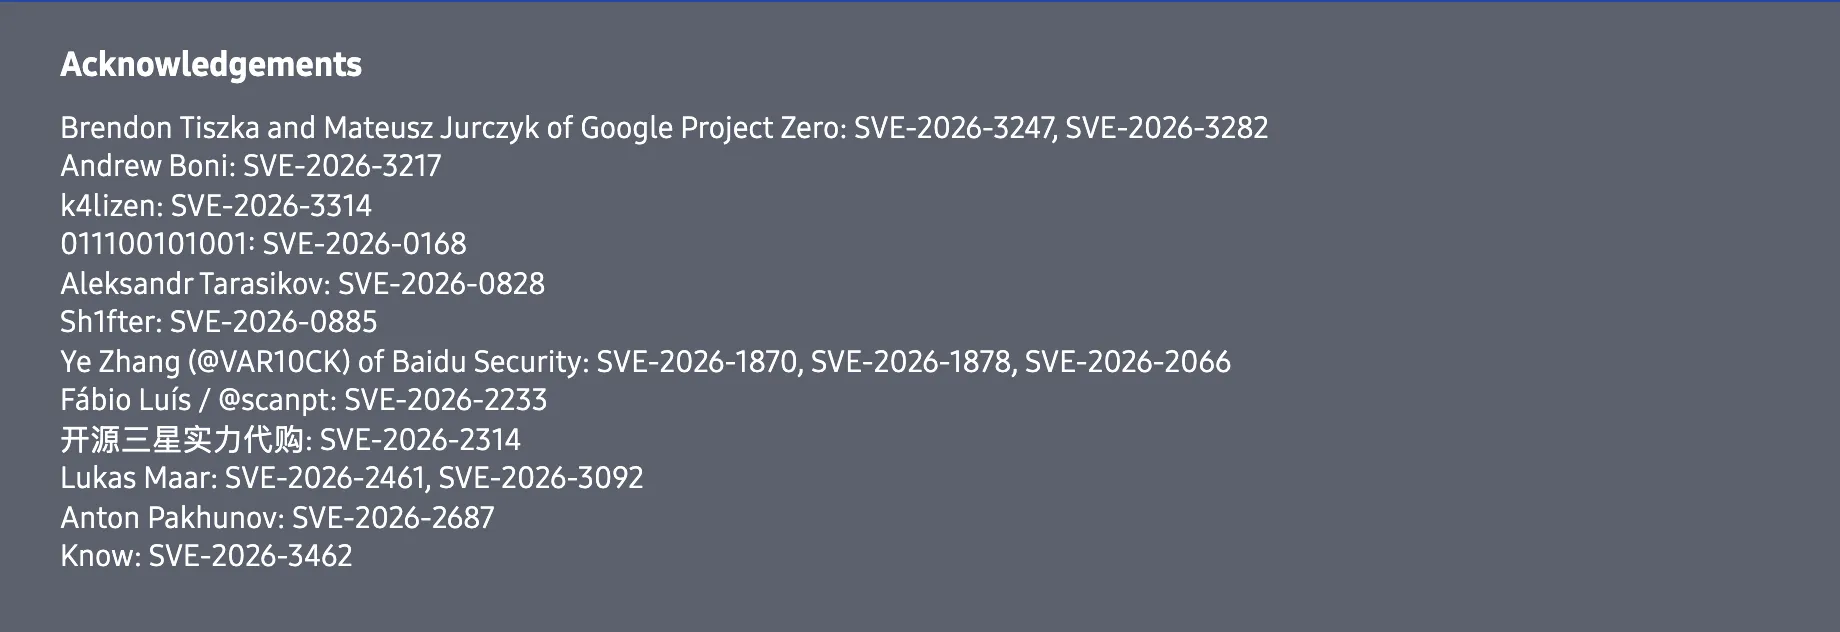
Samsung's September 2026 acknowledgements list, with the line "Andrew Boni: SVE-2026-3217" second from the top
Samsung credits reporters by SVE number rather than by CVE, so SVE-2026-3217 is the line to match.

Timeline#

  • 2026-06: reported to Samsung’s Mobile Security Rewards Program
  • 2026-09-08: fixed in SMR Sep-2026 Release 1; disclosed in Samsung’s bulletin as SVE-2026-3217, with CVE-2026-21094 assigned
  • 2026-09-09: NVD record published
⚠ UNDER CONSTRUCTION since 1997 ⚠
✉ E-MAIL ME! NEW! Sign my guestbook
Chrome 149+ I'd know Best viewed in ANY browser Made with Vim Lynx friendly No AI was harmed Powered by ASCII Valid HTML 4.01 Y2K compliant Press ~ for a shell
⊹ The Lonely Webring ⊹
members: 1 (it's me) · est. 1999
You are visitor 000001

Best viewed in Netscape Navigator 4.0 at 800×600 · home