security
CoreUI: a heap bug in macOS asset decoding
- component
- Heap corruption in CoreUI
- reported
- Apple Security Bounty,
- status
- fixed in macOS Golden Gate 27
- write-up
- generic pass
About the security content of macOS Golden Gate 27 ↗
In May 2026, I reported a heap memory-corruption vulnerability to Apple’s Security
Research program. The vulnerability was in CoreUI, the framework macOS uses to read compiled
asset catalogs: the .car files an app’s icons and images are packed
into. Apple eventually fixed it in macOS Golden Gate 27 in September 2026,
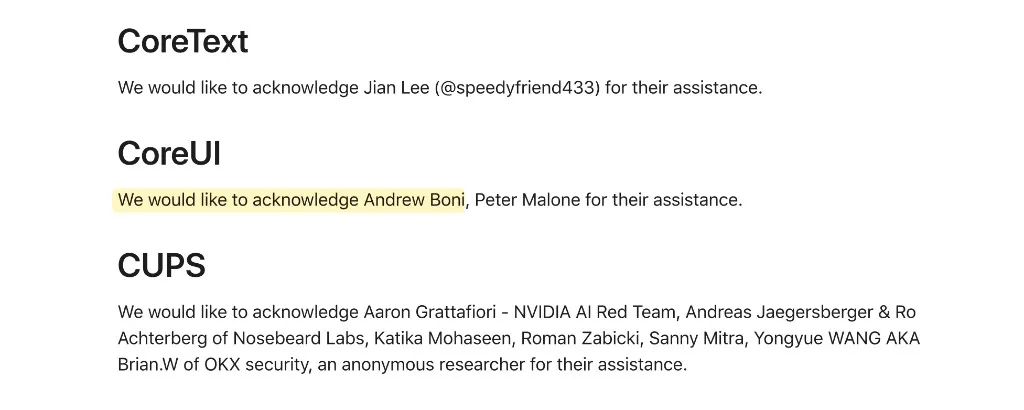
and credited me in the release notes.
The gist of this bug is this: if you build a Mac app, the icons don’t ship as loose files. Instead, they get
compiled into Assets.car, and then CoreUI processes it at runtime. Many of
the images inside are compressed, so CoreUI decompresses them when something needs it. This decoding is where the vulnerability
lives: a file the system opens on your behalf, built by whoever sent you the app, parsed (unsafely) by
macOS framework code.
Timeline#
- 2026-05-23: reported to Apple Security Bounty
- 2026-09-14: addressed in macOS Golden Gate 27; credited under CoreUI in the release’s additional recognition