security
CVE-2026-95339: Use-after-free in Chrome's browser process
- severity
- Critical
- component
- Use-after-free in ServiceWorker (browser process)
- reported
- Google Chrome VRP,
- status
- fixed in Chrome 154.0.8037.57 (stable)
- write-up
- generic pass
Chrome release, Chrome 154 stable ↗ Chromium bug 548585299 ↗ NVD record ↗
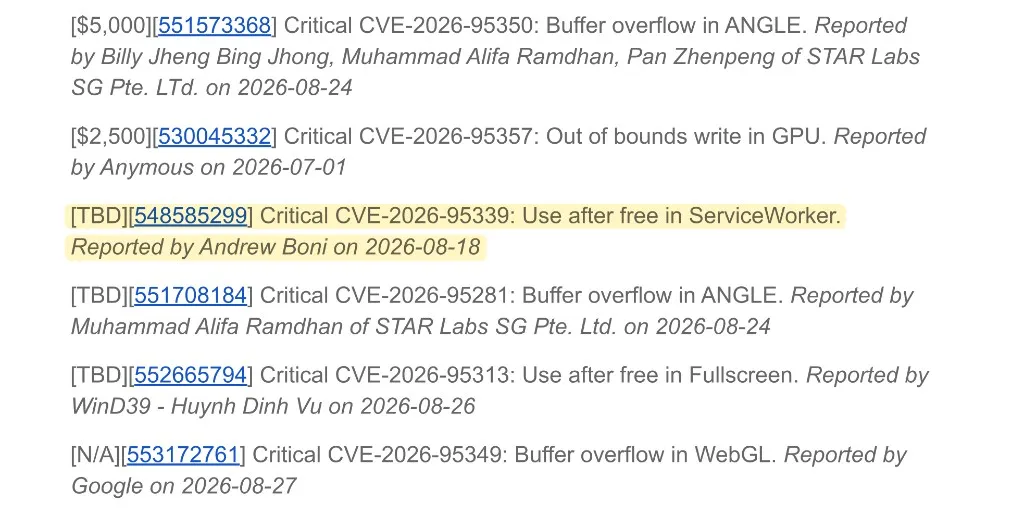
In August 2026 I reported a use-after-free vulnerability to the Chrome VRP. It lives in ServiceWorker, in the browser process, which is the privileged side of Chrome’s sandbox. Google rated it Critical, assigned CVE-2026-95339, and shipped the fix in Chrome 154, which went stable on September 22.
Here’s the advisory:
Timeline#
- 2026-08-18: reported to the Chrome VRP (Chromium issue 548585299)
- 2026-08-20: fix landed in Chromium; I retested against fresh builds and could no longer reproduce it
- 2026-09-09: marked fixed
- 2026-09-17: merged back to the Chrome 152 and 153 release branches (154 already had it)
- 2026-09-21: CVE-2026-95339 assigned
- 2026-09-22: Chrome 154.0.8037.57 promoted to stable; the advisory publishes, rated Critical
- 2026-09-29: NVD record published